


Two master’s students from Chalmers University of Technology have successfully demonstrated a lightweight Zero Trust architecture running on Kvaser Edge hardware, showing that advanced cybersecurity principles can be applied in distributed edge environments without significantly impacting performance.
News
18/09/2026
by Kvaser
Chalmers students demonstrate Zero Trust security for Kvaser Edge devices
As edge devices become increasingly responsible for local data processing and decision-making, organizations face the challenge of enabling centralized management while maintaining strong security. The thesis project explored whether Zero Trust principles could be implemented in a Kubernetes-based edge environment operating on resource-constrained hardware.
Working on a Kvaser Edge WL400S, Angelica Hörngren and Lilly-Ann Stenberg developed and tested an architecture that combined Kubernetes, KubeEdge, SPIRE, Envoy, Open Policy Agent (OPA), EdgeMesh, and Calico to create multiple layers of security controls.
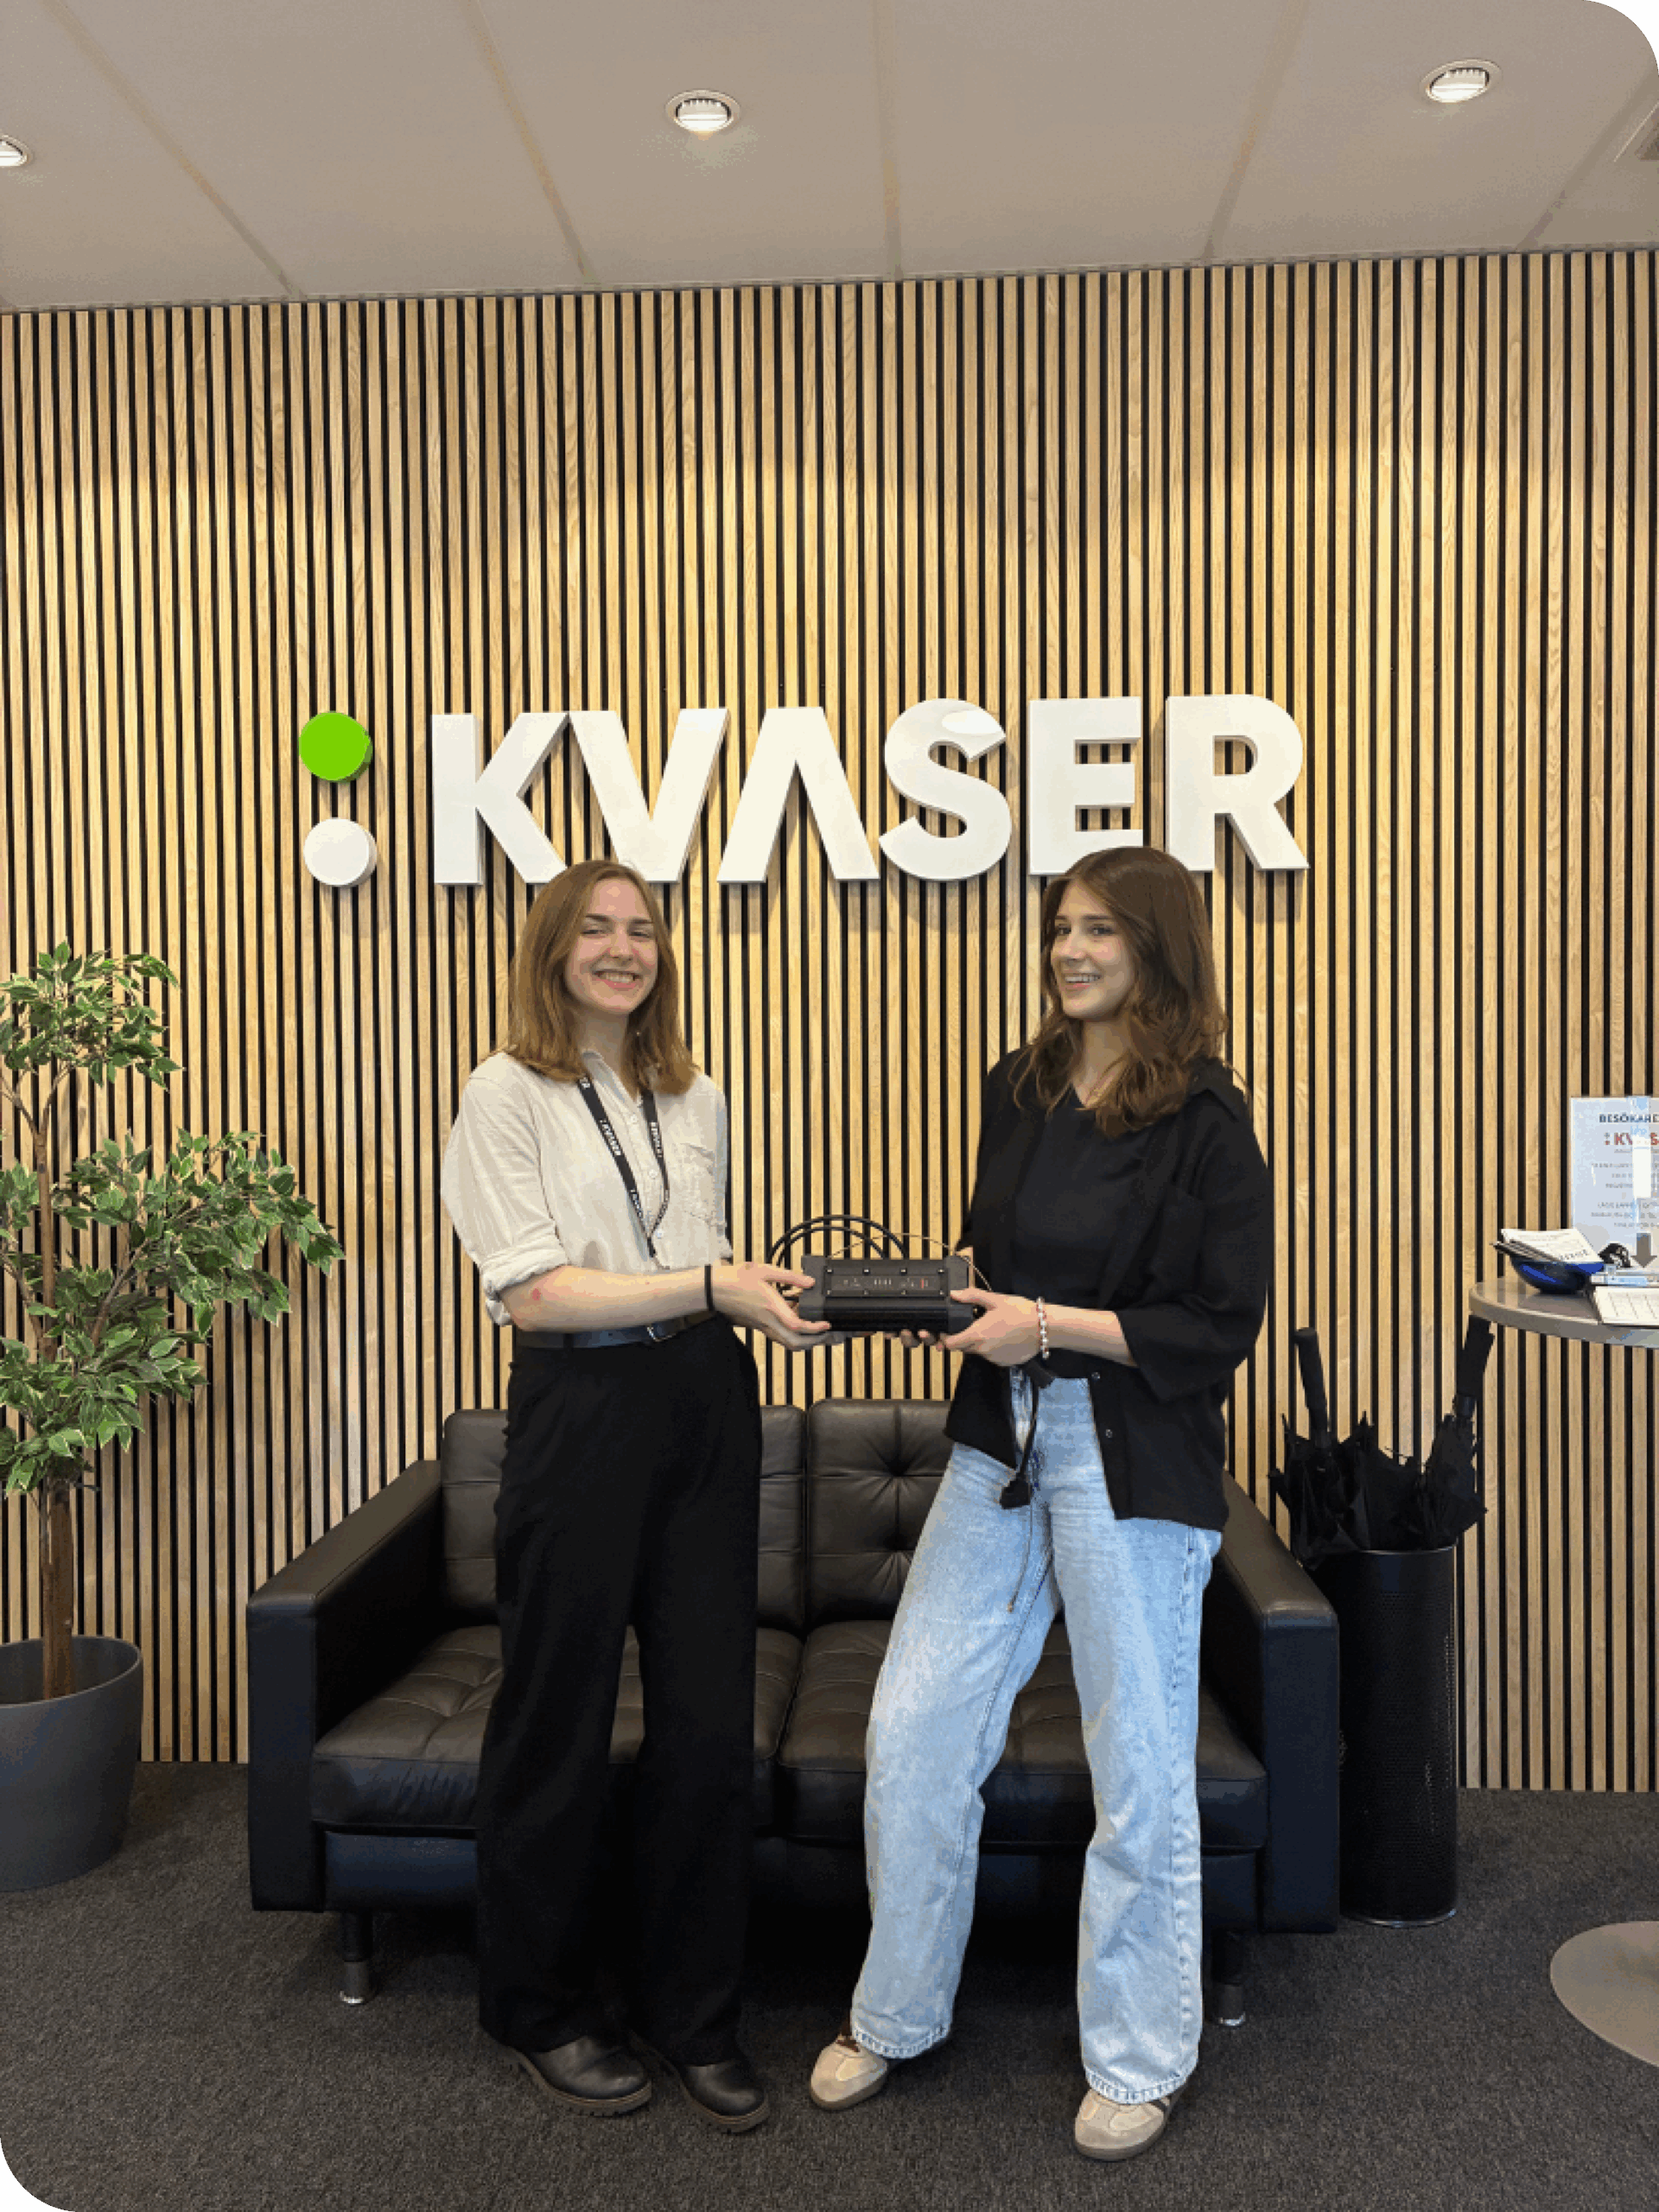
Left to right: Lilly-Ann Stenberg and Angelica Hörngren , Chalmers University of Technology
One of the project’s key achievements was addressing workload identity verification in scenarios where cloud connectivity is unavailable. To overcome this challenge, the students developed a custom SPIRE workload-attestation plugin capable of using local container runtime information when access to Kubernetes control-plane data was not available.
Testing showed promising results. During evaluation, the prototype successfully handled more than 4,000 requests with no failures, while 95% of responses completed in less than 48.67 milliseconds. The results indicated that the additional security controls introduced minimal performance overhead.
The project also demonstrated that backend services could only be accessed through approved authorization pathways, with network policies preventing attempts to bypass security controls.
While additional hardening would be required before production deployment, the research indicates that Zero Trust principles can be implemented effectively in edge computing environments used for industrial and automotive applications.
The work was carried out as part of a master’s thesis project at Kvaser and is expected to be published following Chalmers University’s review and publication process.
Interested in learning more about Angelica and Lilly-Ann’s work? Read their DevBlog about: Implementing Zero Trust on Kvaser Edge
Visit product for product specifications and technical data.

Kvaser Edge WL400S
The Kvaser Edge is a secure, rugged ARM-based Linux computer tailored for demanding real-time data acquisition, edge analytics and seamless cloud integration, all within a compact form factor.
Visit product linkedin
 twitter
 youtube
 youku
 weixin
 1...2...3...