


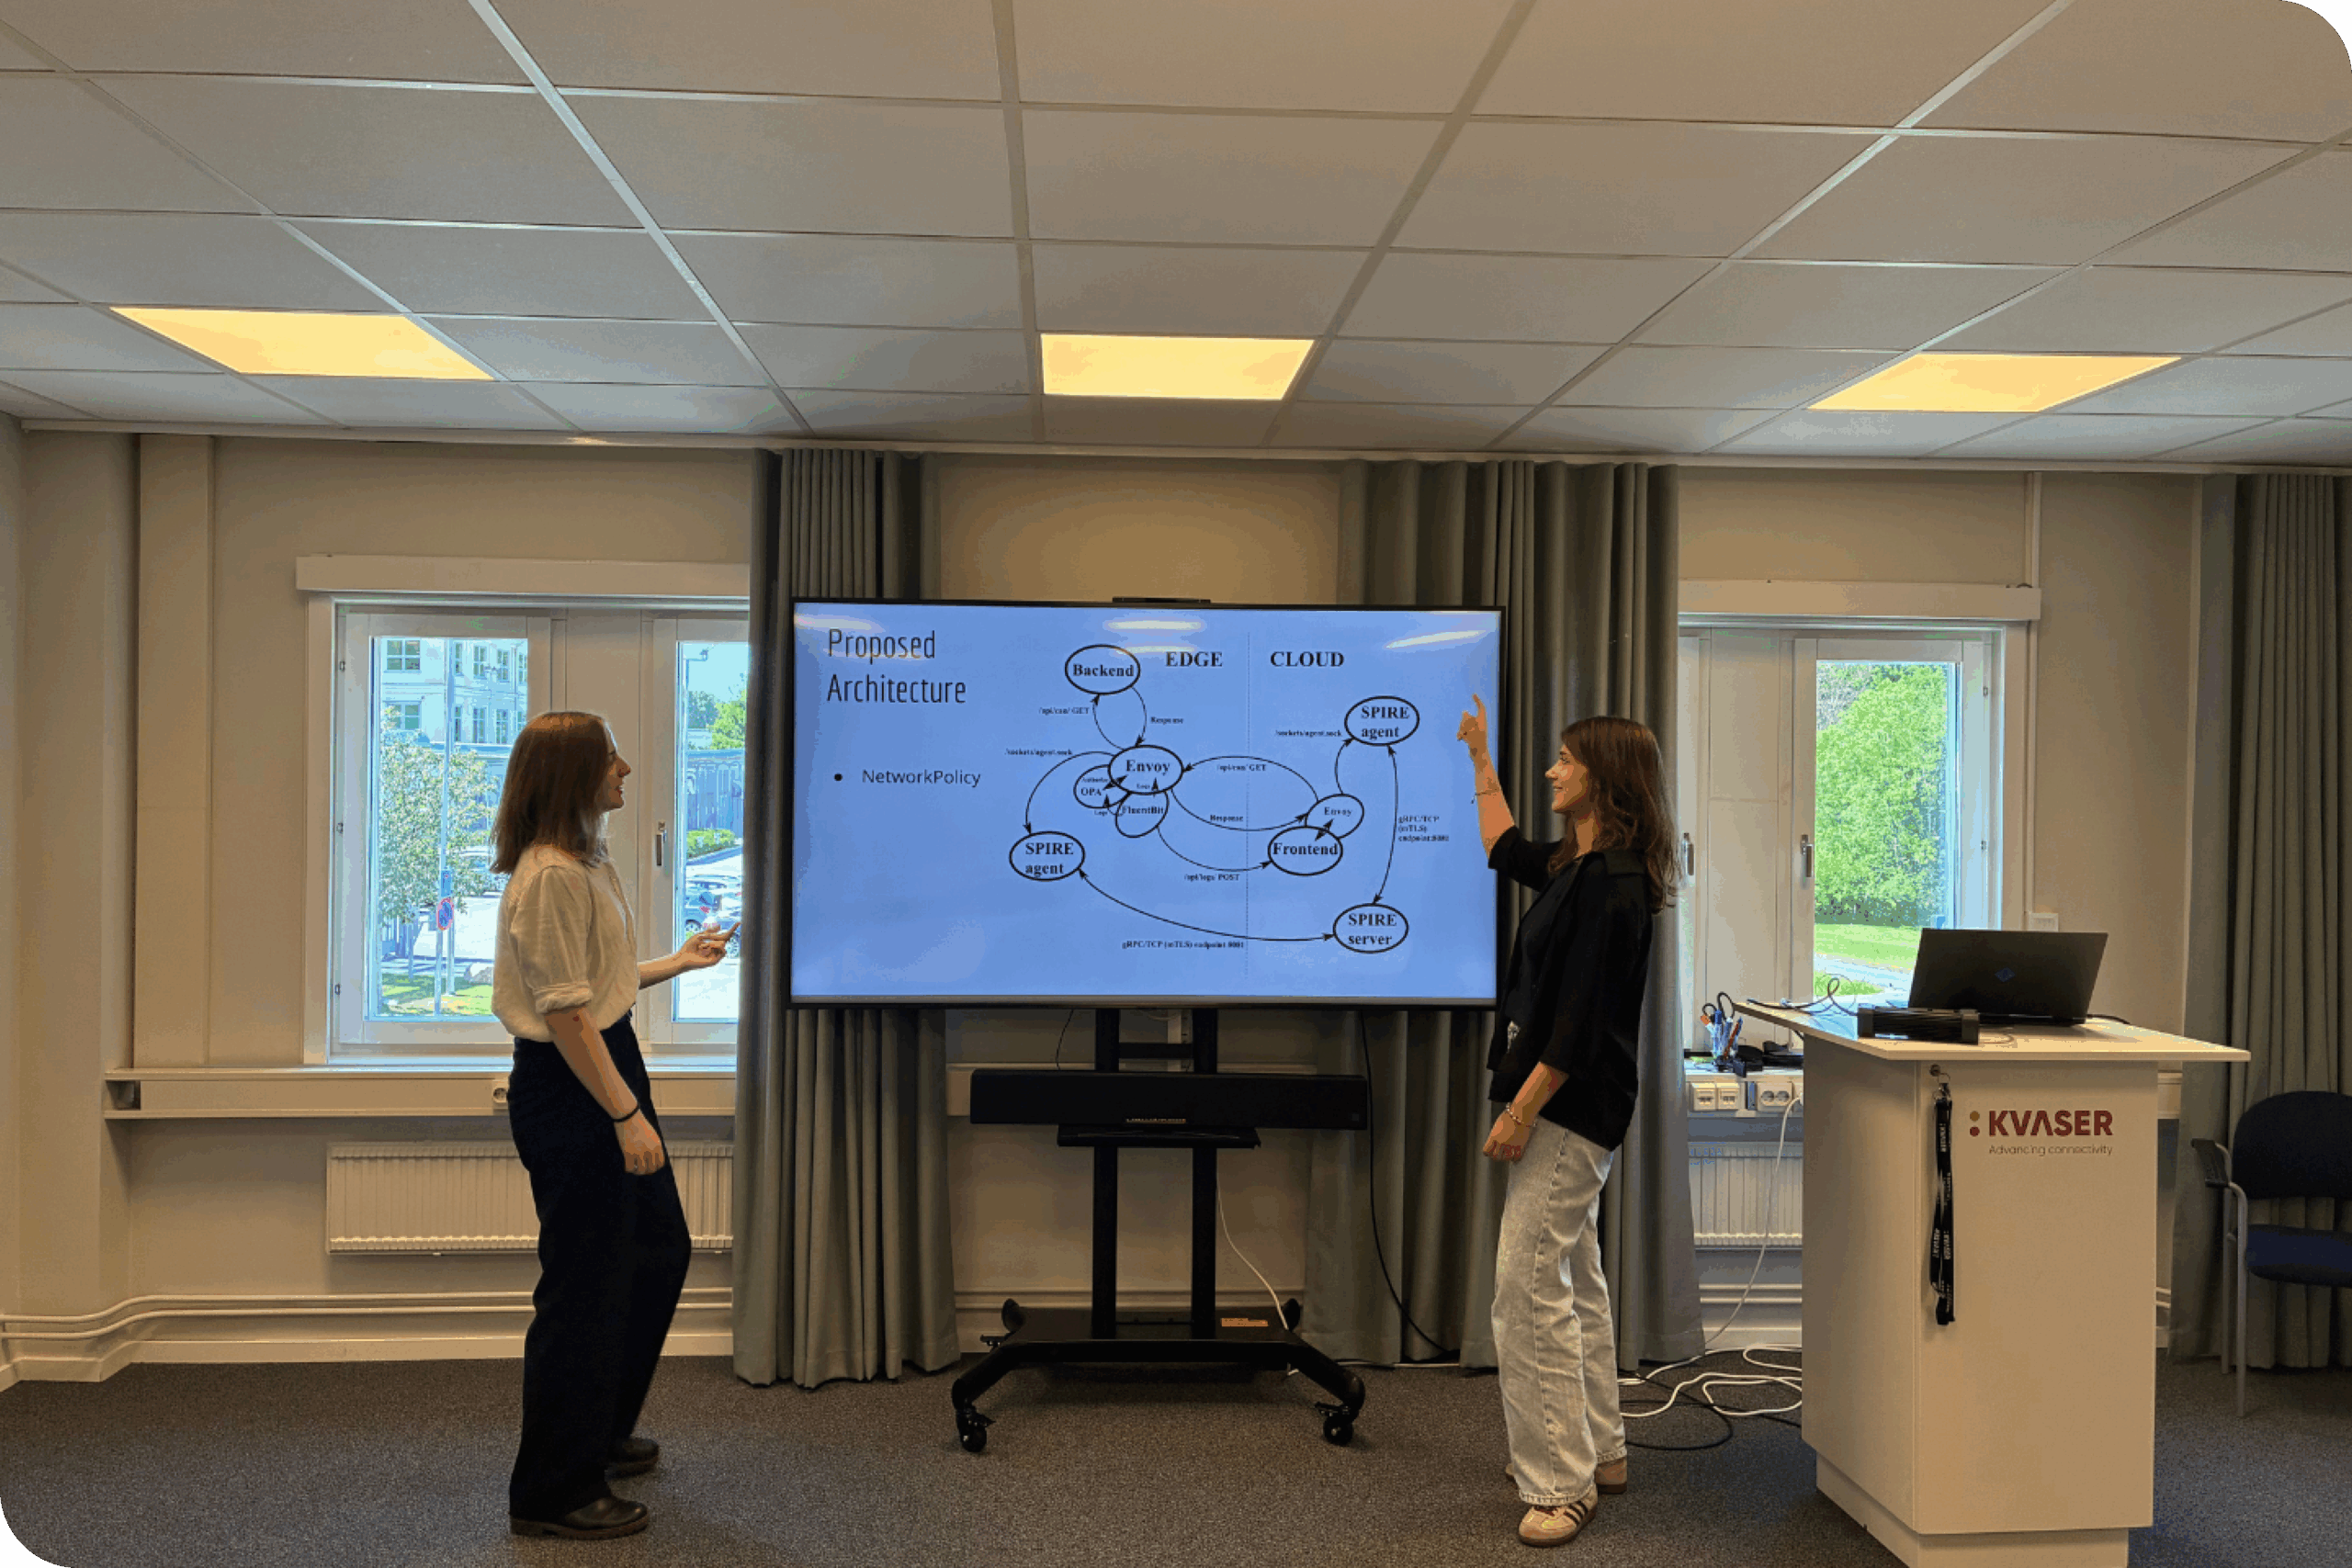
Can a cloud-managed edge device remain secure when connectivity is unreliable and resources are limited? Two master students at Kvaser explored whether Zero Trust principles could be applied to an edge-based Kubernetes environment running on Kvaser Edge hardware. Their master’s thesis project combined Kubernetes, KubeEdge, SPIRE, Envoy, OPA, EdgeMesh, and Calico into a lightweight architecture designed for secure edge deployments.
As edge devices become more capable, they no longer function only as passive data collectors. They can run local applications, process data close to the source, filter what should be sent onward, and continue operating even when connectivity is unreliable. This creates new opportunities for systems that depend on real-time data, particularly in industrial and automotive environments.
At the same time, organizations increasingly want the convenience of centralized management. Connecting edge devices to a cloud-managed platform can simplify deployment, updates, monitoring, and fleet management. However, every new connection also creates a potential attack surface.


 1...2...3...